
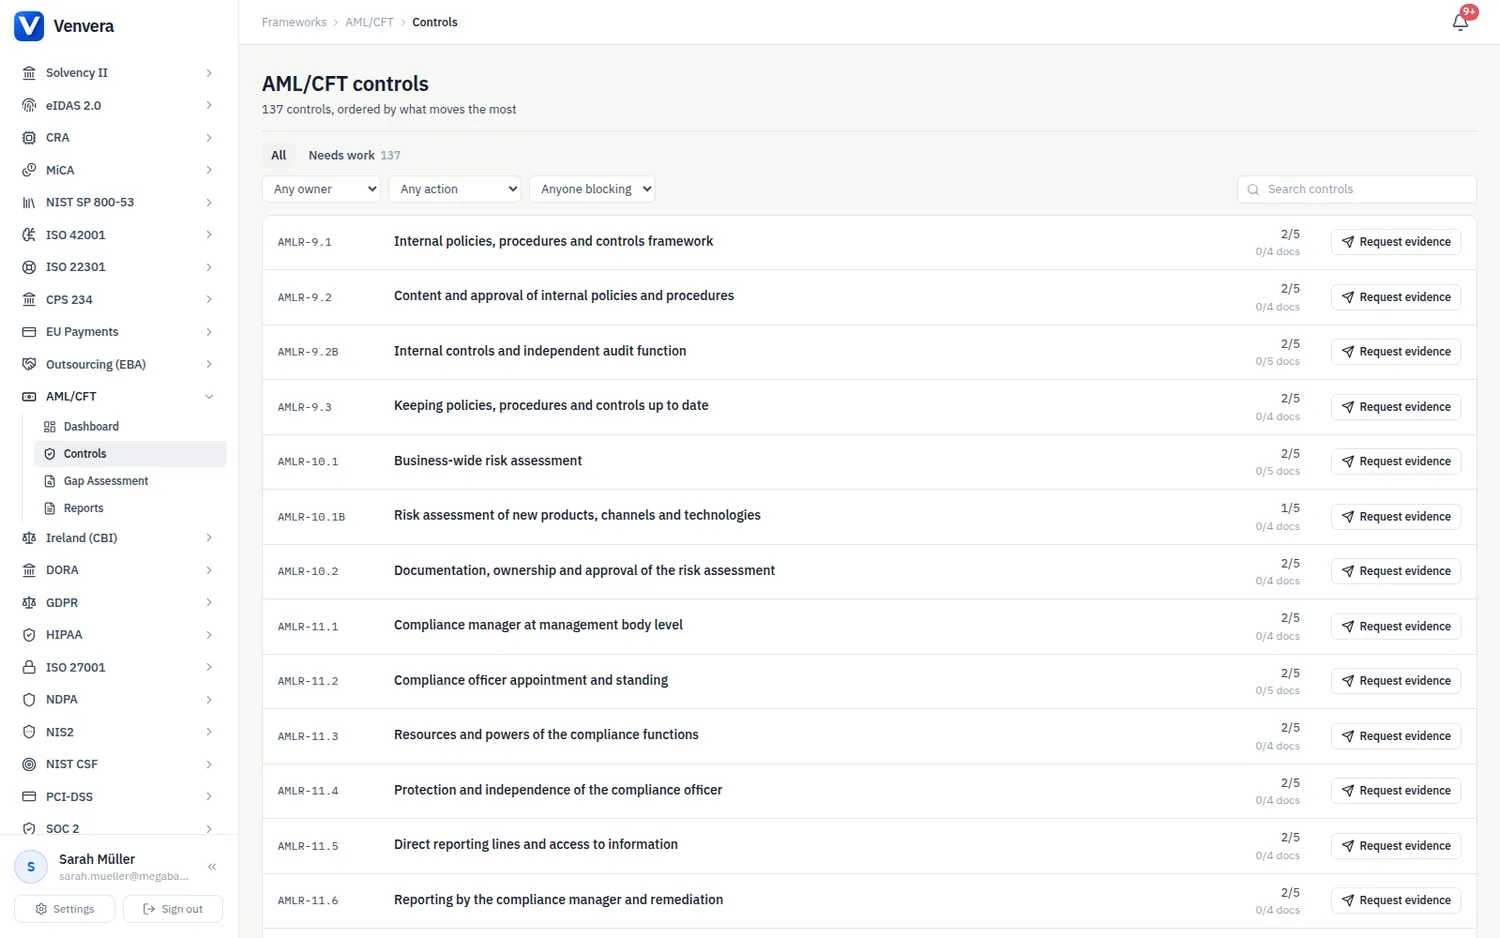
The requirements page lists all 137 duties of the AML/CFT programme. Each carries an implementation status, an owner, implementation notes, evidence and a review date, and each has authored guidance describing the artefacts that satisfy it, what a reviewer rejects, the common gaps and how the expectation scales between a small firm and a large one.
Status values
The same four values used across every Venvera framework: Not Implemented, Partial, Implemented and Not Applicable. Not Applicable has a real role in this module. The Regulation narrows some duties to a class of obliged entity, and the requirement text ends with "Applies to: ..." where it does: e-money issuers, acquirers, crypto-asset service providers, life and investment-related insurers, parents and groups, money remitters and firms using agents, payment initiation and account information service providers. A credit institution marks the e-money and crypto rows not applicable with that reason; an e-money institution marks the correspondent banking rows the same way. A duty that binds every obliged entity has no such sentence and should not be scoped out.
Reading the transition sentence
The AMLR applies from 10 July 2027. Every AMLR requirement that replaces a duty under Directive (EU) 2015/849 ends with the sentence "Until 10 July 2027 the equivalent duty is Article X of Directive (EU) 2015/849 as transposed". Treat that sentence as the citation to use with your national supervisor today, and treat the AMLR article as the citation from 2027. The evidence is the same; only the label changes.
The duties inspections concentrate on
Supervisors read the same programme every firm has and go to the places where the paper and the practice diverge. The guidance on each requirement says what gets rejected; these are the requirements where that happens most often.
| Requirement | What the inspection looks for |
|---|---|
| AMLR-11.1 and EBACO-17 | A named member of the management body as compliance manager, and evidence that material weaknesses reach that person in writing before the annual report, not through it |
| EBARF-1.14 | A business-wide risk assessment built from the firm's own data (customer distribution, corridors, channels, product volumes), not a template narrative |
| EBARF-3.6 | Proof that the customer risk model cannot rate a PEP, a high-risk third country customer or a correspondent respondent as low through weighting, and who can override a score |
| AMLR-26.2 | The refresh intervals per risk tier, the number of overdue files and how trigger events are detected |
| EBARF-4.71 and EBARF-4.75 | Written design decisions behind the monitoring scenarios and thresholds, approval of the detection criteria by the firm rather than the vendor, and the ex post sample reviews that test them |
| AMLR-18.1 and AMLR-18.3 | The outsourcing register with the supervisory notification date before the service start date, and evidence that risk profiles, acceptance decisions and detection criteria are decided or approved by the firm |
| EBARM-15.3 | Calibration tests behind the current matching thresholds and an annual review of screening performance, with the rationale written down |
Event-driven clocks
Several requirements carry a deadline that starts on an event rather than on a date. They are not calendar obligations; the deadline is in the requirement text and the guidance, and the record you keep is the timestamp of the trigger next to the timestamp of the action.
| Trigger | Deadline | Requirement |
|---|---|---|
| Knowledge or suspicion that funds are proceeds of crime | Report to the FIU promptly; the clock starts when the suspicion is formed | AMLR-69.1 |
| Request for information from the FIU | 5 working days, which the FIU may shorten to under 24 hours | AMLR-69.1 |
| A report filed on a transaction | Refrain from executing; if no FIU instruction within 3 working days, execute after a documented risk assessment | AMLR-71 |
| Discrepancy with the beneficial ownership register | 14 calendar days from detection | AMLR-24.1 |
| Deferred verification under simplified due diligence | 60 days from the start of the relationship | AMLR-33.1 |
| Decision to outsource an AML task | Notify the supervisor before the provider starts | AMLR-18.1 |
| New designation under targeted financial sanctions | Rescreen the customer base on the day the list changes | AMLR-26.4, EBARM-15.8 |
| True match against a restrictive measure | Immediate freeze and a report within the competent authority's timeline | EBARM-14.1 |
Evidence
Attach evidence to the requirement it supports. The authored guidance on each requirement lists the artefacts a reviewer asks for and states what gets rejected, so use it as the acceptance test before you attach a document: an approved policy with a scope statement rather than a draft, a minute that records a decision rather than a presentation, a register with the dates that let a reviewer compute the elapsed time. The AML/CFT requirements are not on the crosswalk: they are duties of an obliged entity under the AMLR and the EBA guidelines, and the similar-sounding controls elsewhere (personnel screening in ISO 27001, conflicts of interest in MiCA, retention and deletion in the GDPR) evidence a different duty. Where one document genuinely answers both, attach it to each requirement.